Ahrefs Domain Rating set in type 3 Nov 2026, reset 27 Oct 2026.
Autonomous security operations platform that investigates every alert to a verdict and acts in existing security tools, improving continuously.
The story so far
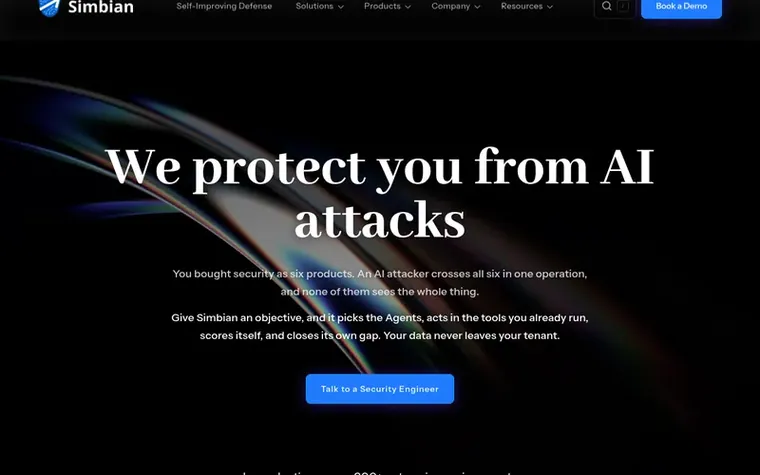
Homepage of Simbian®
Simbian® is an autonomous security operations platform that protects enterprises from AI attacks. Rather than operating as separate products, it functions as one unified system where you set an objective and its AI Agents decide which tools to run and what actions to take within your existing security infrastructure.
The platform reads from over 100 sources including SIEM, EDR, XDR, identity tools, and vulnerability feeds, then reasons across all signals to investigate alerts to a verdict. It acts directly in the tools you already own—your EDR, cloud, Active Directory, and SIEM—closing the loop by filing tickets in your ITSM. The platform learns from every analyst correction and improves continuously, with 95% of proposed actions approved by your own team.
Simbian® operates across 300+ enterprise environments and is designed to handle the speed of AI-driven attacks that conclude in seconds, long before traditional tools or humans can react. The platform includes specialized AI Agents for SOC operations, threat hunting, penetration testing, and network security operations, all sharing a persistent Context Lake that stores your organization's assets, identities, and past verdicts.
Typeset features
Acts directly in EDR, cloud, Active Directory, and SIEM
Investigates every alert to a verdict with reasoning, not playbooks
AI SOC Agent for automated alert triage and response
AI Threat Hunt Agent for hypothesis-driven threat detection
AI Pentest Agent for continuous, on-demand offensive testing
AI NetSecOps Agent for firewall and network operations
Context Lake for organization-wide persistent memory of assets and verdicts
Multi-tenant isolation with per-tenant reasoning for MSSPs
Hardened against prompt injection and data poisoning
Pricing
Pricing model: Contact for pricing
Simbian® metrics
Set in type for simbian.ai: Ahrefs Domain Rating and Majestic link data, with the change since the last edition.
Metric
Value
Domain Rating
44● no change since last check
Trust Flow
17● no change since last check
Citation Flow
36● no change since last check
Referring domains
356● no change since last check
External backlinks
1,838● no change since last check
Ahrefs Domain Rating set in type 3 Nov 2026, reset 27 Oct 2026. Lead topic: Business/Financial Services (17). Majestic set 27 Oct 2026, reset 27 Oct 2026. Link data typeset by Majestic. Trust Flow, Citation Flow and Topical Trust Flow are trademarks of Majestic-12 Ltd.
Simbian® domain colophon
Read the colophon
From the registry's public RDAP record, checked 1 Nov 2026, 09:46 UTC.
Measured after Simbian® went live on Zivaro Launch on 27 October 2026.
Domain Rating (Ahrefs)
44● no change since launch
44 at launch (27 Oct 2026), 44 on 2 Nov 2026
Referring domains (Majestic)
356
First measured 27 Oct 2026
Day 7 since launch. Next receipt: day 30, 26 Nov 2026. These are measurements, not proof of cause: many things move these numbers. Figures we have not measured are left out.
SOAR runs preset playbooks that must be written, forked per tenant, and maintained forever. AI SOC reasons from each tenant's environment without playbook maintenance. Simbian®'s AI SOC Agent investigates across tools, learns from analyst corrections, and closes every alert end-to-end, allowing MSSPs to scale clients without scaling engineers.
How fast can an MSSP onboard a new tenant on Simbian®?
Onboarding takes hours, not months. The Context Lake ingests the tenant's SIEM, EDR, identity stack, and SOPs the same week the SOW closes. Agents go live with per-tenant context already in place.
How does multi-tenant context isolation work in Simbian®'s AI SOC?
Every tenant gets a dedicated Context Lake that holds their telemetry, escalation rules, SOPs, and analyst feedback. Simbian®'s agents only reason on the requesting tenant's data, so verdicts, learnings, and history never cross client boundaries.
What is an AI SOC for MSSPs?
An AI SOC for MSSPs is an autonomous security operations platform that runs Tier-1 and Tier-2 alert triage end-to-end across every tenant, with per-tenant context isolation built in. Simbian®'s AI SOC Agent opens the ticket, pulls cross-tool evidence from each tenant's Context Lake™, applies the verdict, and closes the alert with a full audit trail. One control plane covers every client without sharing reasoning across tenants.
How does AI SOC for MSSPs differ from SOAR?
SOAR runs preset playbooks. AI SOC reasons from each tenant's environment. Playbooks have to be written, forked per tenant, and maintained forever, and they still miss novel attacks at 2 a.m. Simbian®'s AI SOC Agent investigates across tools, learns from analyst corrections, and closes every alert end-to-end without playbook maintenance, so MSSPs drop the playbook tax and scale clients without scaling engineers.
Leave a review for Simbian®
No review of Simbian® set in type yet. Set the first.
 Kimchi Coding
 Rigorix
 Verdict
 rightcommit